XBOW
XBOW is an autonomous offensive security platform that pentests web apps and APIs and reports only findings it has proven with a working exploit.
Overview
XBOW
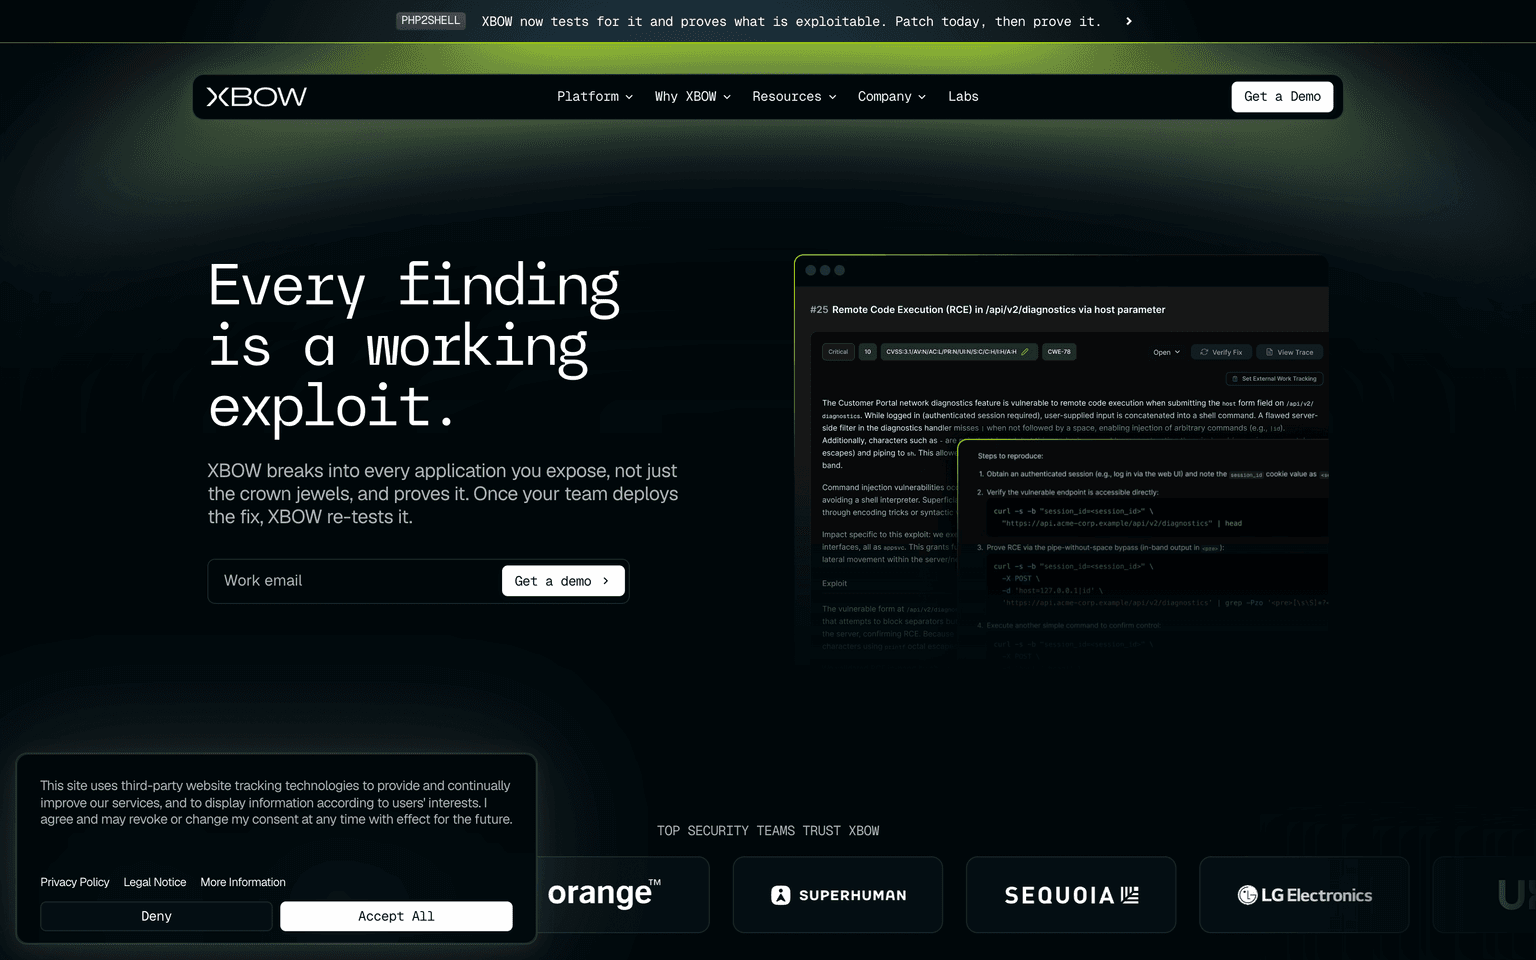
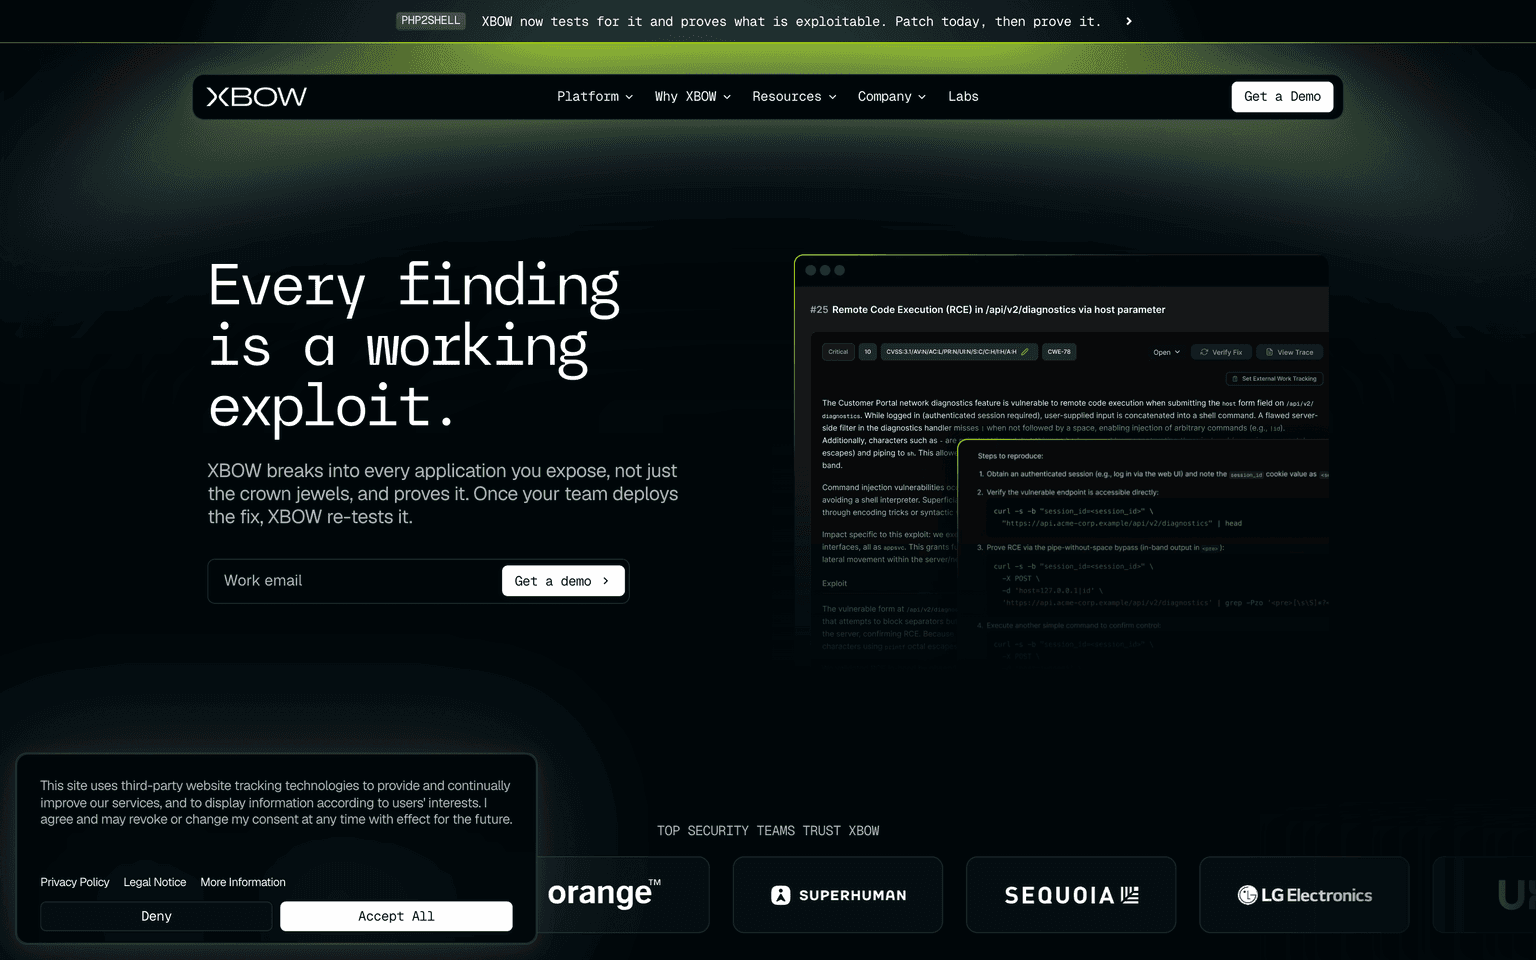
XBOW is an autonomous offensive security platform that runs penetration tests against web applications and APIs without a human driving the attack. Thousands of XBOW agents probe targets in parallel, chain flaws together, and report only what they actually broke into, so each finding arrives with the working exploit, the request and response, and the steps to reproduce it. Once a fix ships, XBOW re-tests the issue and marks it closed when the exploit no longer works. It runs continuously or on demand rather than as a yearly engagement.
Production credibility: XBOW's record is public: it says it was the first autonomous system to rank #1 on HackerOne, with more than 1,500 reproducible exploits on production targets, and that it found and proved three critical Microsoft CVEs on its own, earning a place on Microsoft's MSRC leaderboard. In October 2026 an XBOW researcher working with its agents chained three unknown Chrome bugs into a full sandbox escape in six days, which Google rewarded with its first $250,000 full-chain payout of the year. XBOW cites a Fortune 50 organisation that assessed 180 applications in a month and received 1,216 validated findings, and says more than 200 security teams use it; Moderna and Superhuman security leads are quoted on its site. It lists SOC 2, ISO 27001, ISO 42001, PCI DSS and NIS 2 compliance and does not train models on customer data. Pricing is usage-based and scoped to your environment by quote, with re-tests free and unlimited; XBOW is also sold through the AWS, Google Cloud, Oracle and Microsoft marketplaces.
Key Features
- Autonomous pentesting of web applications and APIs by many agents in parallel
- Every finding ships with a working exploit, request, response and reproduction steps
- Free, unlimited re-tests that confirm a fix closed the issue
- Scope, impact level, protected URLs, rate limits and testing windows set by you
- Command checker that blocks destructive actions, with every action logged
- Findings pushed to ticketing systems with code-specific fix suggestions
Ideal Use Case
Application security teams that own more apps than they can pay humans to test. Instead of a yearly pentest on the few most important systems, they point XBOW at everything they expose, run it on each release, and hand developers findings that are already proven exploitable, which cuts the triage time spent on scanner noise.
How XBOW differentiates
Scanners and static analysis report possible vulnerabilities; XBOW reports only ones it has exploited, which is its main argument against both DAST tools and traditional pentest firms. Horizon3.ai's NodeZero is the closest match but centres on internal networks and infrastructure, while XBOW centres on web applications and APIs. RunSybil also sells continuous AI pentesting. XBOW has no self-serve plan or public price list.
FAQ
Q: What is XBOW? A: XBOW is an autonomous offensive security platform. Its AI agents run penetration tests against your web applications and APIs and report only vulnerabilities they have proven with a working exploit.
Q: How much does XBOW cost? A: XBOW does not publish prices. Pricing is usage-based and scoped to your environment, so you request a quote; re-tests of fixed findings are free and unlimited. It is also available through the AWS, Google Cloud, Oracle and Microsoft marketplaces.
Q: Is XBOW safe to run against production? A: XBOW says it uses production-safe checks designed not to modify data, a command checker that blocks destructive actions, and scope, rate limit and testing-window controls that you set. Every action is logged.
Q: Did XBOW really reach #1 on HackerOne? A: XBOW states it was the first autonomous system to rank #1 on HackerOne, with more than 1,500 reproducible exploits on production targets.
Q: How is XBOW different from a vulnerability scanner? A: A scanner flags possible issues. XBOW attempts the attack and only reports what it broke into, attaching the exploit and reproduction steps, then re-tests after you deploy a fix.
tl;dr
XBOW is an autonomous AI pentesting platform for web applications and APIs that reports only vulnerabilities it has exploited and re-tests fixes for free. It reached #1 on HackerOne by its own account; pricing is usage-based and quoted per environment.
Why Use XBOW
User Reviews
Similar Tools


