Semgrep
Semgrep is a code security platform that combines rule-based static analysis with AI triage across SAST, dependency scanning and secrets.
Overview
Semgrep
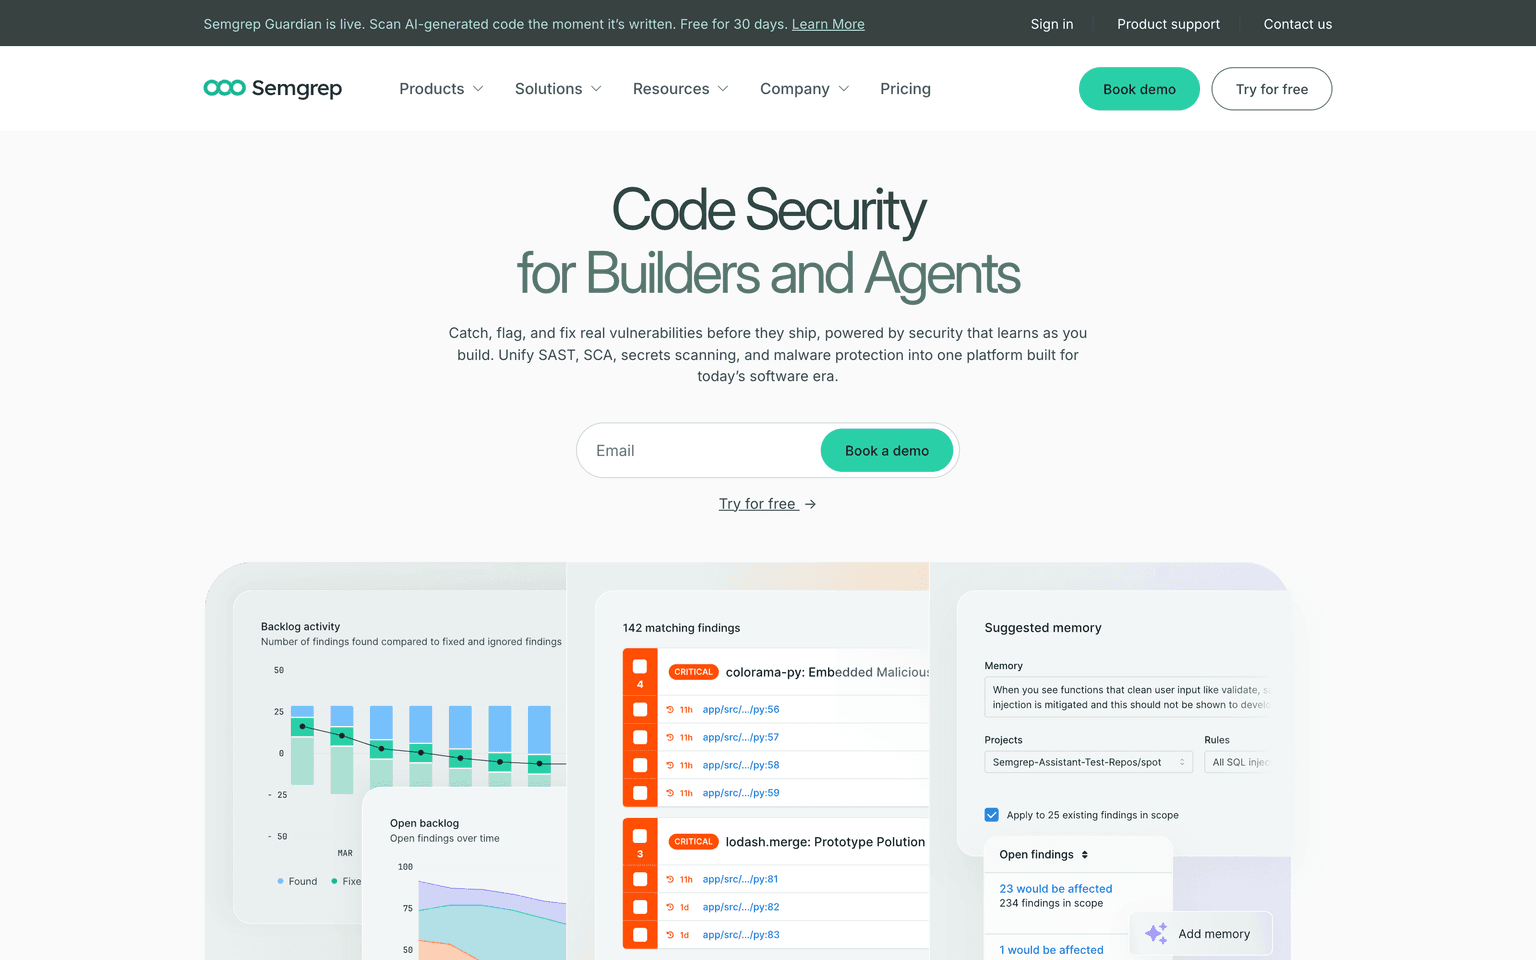
Semgrep is a code security platform that finds vulnerabilities in your own code (SAST), in open-source dependencies (SCA) and in hardcoded secrets, and blocks malicious packages before they reach a machine. Semgrep pairs its rule-based static analysis engine with AI reasoning, which it uses to catch logic flaws such as broken authorization, filter out false positives and suggest fixes in pull requests and IDEs. The engine began as an open-source project, and the Community Edition is still free to run under the LGPL-2.1 licence.
Production credibility: Semgrep announced a $100 million Series D led by Menlo Ventures on its own site. It reports more than 75 million scans a year and over 3,000 community rules in its public registry, and the open-source engine on GitHub has more than 17,000 stars. Its headline AI figures are its own: 96% agreement between security reviewers and its AI triage across more than 6 million findings, and 3.5 times more true positives than using AI alone. Vanta, Thinkific and Acrisure engineers are quoted on its homepage. Pricing on its own page: a Free edition for up to 10 contributors and 10 private repositories, with cross-file Pro rules and 60 AI credits; Teams starting at $30 per contributor a month for Code or Supply Chain and $15 for Secrets, with SSO and up to 500 private repositories; and custom Enterprise plans with on-prem source control and dedicated infrastructure. A contributor is anyone who committed to a scanned private repository in the last 90 days.
Key Features
- Static analysis across more than 35 languages with cross-file and taint analysis
- Supply chain scanning with reachability analysis, SBOM export and malicious dependency detection
- Secrets detection with semantic analysis and validation of live credentials
- AI triage that remembers past decisions so repeat false positives stay suppressed
- Fix suggestions in pull requests, VS Code and JetBrains, plus MCP integrations for AI coding tools
- Custom rules written in a syntax that mirrors the code being searched
Ideal Use Case
Engineering and AppSec teams that want one tool for code, dependency and secrets scanning that runs in CI and comments on pull requests. Teams writing a lot of AI-generated code can add Semgrep Guardian to scan that code as it is written, and security engineers who need checks specific to their own codebase can write custom rules without learning a query language.
How Semgrep differentiates
Against Snyk, Semgrep's pitch is its rule engine: custom rules look like the code they match, and the core engine is open source, so teams can run it locally with no account. Sonar focuses on code quality as much as security, while Semgrep is security-first. Socket specialises in malicious open-source packages; Semgrep covers that alongside SAST and secrets in one platform. The free tier's 10-contributor cap means most companies will pay.
FAQ
Q: What is Semgrep? A: Semgrep is a code security platform covering static analysis of your code, scanning of open-source dependencies, secrets detection and malware blocking, with AI used for triage and fix suggestions.
Q: Is Semgrep free? A: Yes. The Free edition covers up to 10 contributors and 10 private repositories, and the open-source Community Edition engine is free under the LGPL-2.1 licence. Teams starts at $30 per contributor a month.
Q: Is Semgrep open source? A: The core Semgrep engine is open source on GitHub under LGPL-2.1. Pro rules, cross-file analysis in the managed platform, and the AI features are part of the commercial product.
Q: Does Semgrep send my source code to its servers? A: If Semgrep runs locally or entirely in your CI pipeline, it says only run metadata is sent. If you opt in to AI features, part of the file containing a finding is sent to a model, and model vendors may not train on it.
Q: How does Semgrep compare with Snyk? A: Both cover SAST, SCA and secrets. Semgrep emphasises custom rules and an open-source engine; Snyk offers a broader platform that also includes container, IaC and DAST scanning. A trial on your own repositories is the best test of noise levels.
tl;dr
Semgrep is a code security platform for SAST, dependency scanning and secrets detection, built on an open-source rule engine with AI triage on top. The Free edition covers up to 10 contributors; Teams starts at $30 per contributor a month.
Why Use Semgrep
User Reviews
Similar Tools